AI endpoint security has become one of the defining shifts in enterprise cybersecurity. For decades, antivirus tools protected devices by matching files against a database of known threat signatures. If a threat was in the database, it was blocked. If it was not, it passed through. Attackers now automate reconnaissance, use polymorphic malware that changes its signature on every run, and exploit vulnerabilities before any signature exists. Signature matching alone cannot keep up, which is why AI endpoint security matters.
The practical response is defence that looks at behaviour, learns what normal activity looks like, and acts quickly when something deviates. That is what modern AI endpoint security platforms are built to do. This guide explains how they work, the four layers they combine, and how to deploy them across distributed, cloud-heavy environments.
Key Takeaways
- Signature antivirus misses zero-day exploits, polymorphic malware and fileless attacks, so AI endpoint security focuses on behaviour instead.
- Behavioral AI security builds a baseline of normal activity and flags deviations, whether or not they match a known threat.
- A modern stack combines four layers: next generation antivirus, endpoint detection and response, extended detection and response, and AI-assisted security operations.
- Autonomous response can isolate devices and stop malicious processes quickly, but humans should govern high-impact actions.
- Zero trust, identity protection and securing AI workloads are the trends shaping AI endpoint security in 2026.
Why Traditional Antivirus Can No Longer Protect Endpoints
Traditional antivirus was designed for a world where malware was relatively stable. It scans files against a dictionary of known malicious signatures. That model has three gaps that attackers exploit:
- Zero-day exploits target vulnerabilities before any signature exists, so signature tools have nothing to match.
- Polymorphic malware rewrites its own code on each execution, so past samples do not protect against the next one.
- Fileless attacks run in memory or abuse legitimate system tools, leaving no malicious file to scan.
AI endpoint security addresses all three. It analyses behaviour rather than files. It compares activity with a continuously updated baseline rather than a static list. It can respond automatically in seconds instead of waiting for an analyst. This is not a small upgrade to antivirus. It replaces the mechanism that antivirus depends on.
The MITRE ATT&CK knowledge base is a useful way to see why. It catalogues attacker techniques, many of which use legitimate tools and leave no unique file signature. Detecting them requires watching behaviour.
What Is AI Endpoint Security?
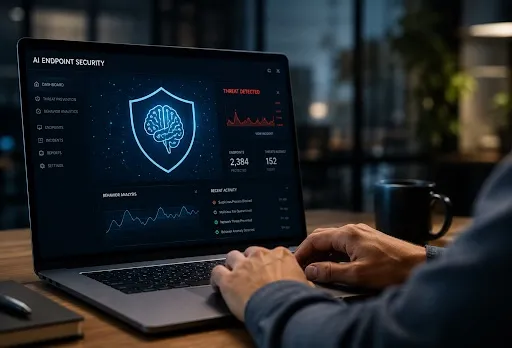
AI endpoint security uses machine learning, behavioural analytics and automation to monitor, detect and respond to threats on endpoints. Endpoints include laptops, desktops, servers, mobile devices and cloud workloads. Increasingly they also include IoT and operational technology devices.
Instead of a list of known bad files, these platforms learn what normal looks like for each user, device and application. When behaviour drifts from that baseline, even subtly, the system raises an alert or acts. It does not matter whether the activity matches a known signature.
On-Device and Cloud-Based AI
AI endpoint security platforms usually run in two configurations, often combined:
- On-device AI runs models directly on the endpoint. It can detect and respond even when the device is offline. That matters for remote staff, branch offices and environments with unreliable connectivity.
- Cloud-based AI sends telemetry to a central platform. There, it is analysed against large threat intelligence datasets and patterns seen across many customers.
Most mature deployments use both. On-device models handle immediate response. Cloud analytics provide deeper investigation and global context. When evaluating vendors, our team recommends testing how each platform behaves with no network connection, because architectures differ.
The 4 Layers of AI Endpoint Security
A modern AI endpoint security stack combines four layers. Each one builds on the one below.
| Layer | What it does | Main benefit |
|---|---|---|
| 1. NGAV | ML-based malware prevention | Blocks unknown malware |
| 2. EDR | Records and investigates endpoint activity | Deep visibility |
| 3. XDR | Correlates endpoint, identity, email, cloud | Cross-surface detection |
| 4. AI SOC | Automates triage and containment | Faster response |
The sections below cover each AI endpoint security layer, starting with the detection method that ties them together.
Behavioral AI Security: How Modern Detection Works
Behavioral AI security is what makes modern platforms different from the tools they replace. These platforms model normal endpoint activity. They watch process execution, network connections, file operations, memory access, logins and application behaviour. Machine learning builds a dynamic baseline for each device and user.
When activity departs from that baseline, the system flags it. Examples include a process spawning unexpected child processes, a user reading data at unusual hours, or an application calling a server it has never contacted. The flag can trigger an investigation or an automated response.
Predictive Detection
Advanced behavioral AI security platforms look for attack precursors, not only completed attacks. Security teams call these indicators of attack. They are sequences of behaviour that tend to come before specific attack types. When a matching sequence appears, the platform can alert or act before the attack completes. This moves AI endpoint security from pure response toward prevention.
Autonomous Response
Behavioral AI security platforms also respond automatically. Common response actions include:
- Process termination, stopping a malicious process before it spreads.
- Network isolation, cutting an infected device off from the network.
- Ransomware rollback, restoring encrypted files on platforms that support it.
- Credential revocation, disabling a compromised identity when suspicious use appears.
Attacks can move fast, so automated containment is increasingly a baseline requirement. Ransomware is a clear example. The CISA StopRansomware resources describe why rapid detection and isolation matter.
Layer 1: Next Generation Antivirus
Next generation antivirus is the foundation of a modern AI endpoint security stack. It replaces signature scanning with machine learning models trained on large sets of malicious and benign files. Next generation antivirus can detect known and unknown malware, polymorphic variants, packed executables and evasive threats. It does not depend on daily signature updates.
The models identify malicious intent from structure and behaviour, not from a specific file hash. That is why next generation antivirus can catch malware that has never appeared in any signature database. The difference is clearest with zero-day attacks, where signature tools are blind by definition.
For enterprises with mixed estates, next generation antivirus gives one consistent baseline. It can cover older Windows servers and modern cloud workloads without separate signature processes. Our DevOps and cloud engineering teams help clients choose configurations that fit their workloads and compliance needs.
Layer 2: Endpoint Detection and Response
Endpoint detection and response adds visibility and investigation depth. EDR records process executions, file changes and network activity across monitored endpoints. Analysts can search this record during incidents or proactive threat hunting.
AI speeds up endpoint detection and response workflows. It triages alerts, correlates related events across devices and surfaces the highest-priority threats first. Human analysts can then spend their time where it matters.
Attack Chain Visualisation
Alert fatigue is a major problem in security operations. Older tools generate many isolated alerts that analysts must correlate by hand. Endpoint detection and response platforms with AI correlation group related events into one attack chain. The view runs from initial compromise through lateral movement, staging and exfiltration.
Major vendors offer this capability. SentinelOne calls its version Storyline, and CrowdStrike provides it in Falcon Insight. Our CrowdStrike vs SentinelOne comparison looks at the differences in more detail. A single storyline is much faster to understand than dozens of separate alerts.
Layer 3: Extended Detection and Response
Extended detection and response takes the EDR model beyond the endpoint. It correlates telemetry from network, email, cloud, identity and application layers in one platform. Attackers often move across several of these surfaces in a single campaign. Separate tools struggle to connect the dots.
AI is what makes extended detection and response workable at enterprise scale. It correlates large volumes of data from many sources and detects patterns that span endpoint, identity and network. Human analysts working across separate consoles could not match that speed.
Identity Threat Detection
Identity is now a primary attack vector, so AI endpoint security cannot stop at the device. Extended detection and response platforms with identity threat detection watch directory services such as Active Directory and Microsoft Entra ID. They look for credential abuse, privilege escalation and lateral movement. Models trained on normal identity behaviour flag unusual access times, impossible travel and abnormal privilege use.
Non-human identities need the same attention. Service accounts, API keys and AI agent identities often hold privileged access and run all the time. Monitoring them closes a gap that pure endpoint tools leave open. For organisations under GDPR or similar privacy laws, this monitoring also supports audit and compliance requirements.
Layer 4: The AI SOC and Autonomous Security Operations
The most advanced AI endpoint security deployments combine behavioral AI security, endpoint detection and response and extended detection and response into an AI-assisted security operations model. AI agents handle routine triage, enrichment and containment. Human analysts supervise. They focus on complex incidents, strategic threat hunting and governance.
This model helps organisations that work across time zones without enough staff for round-the-clock human coverage. Automation handles volume and speed. People handle the decisions that need context. Our team designs integrations that connect these platforms to existing SIEM, SOAR and identity tools, so response workflows run consistently. Managed support engineering services can provide the human layer for teams without a full in-house SOC.
2026 Trends Shaping AI Endpoint Security
Four trends are shaping how AI endpoint security develops this year.
Zero Trust Integration
Zero trust means no device or user is trusted by default, even inside the network. NIST describes the model in SP 800-207. AI continuously checks device health, user behaviour and context to make access decisions. Endpoint posture feeds directly into access policy. Our zero trust implementation guide covers the rollout in detail.
Agentic AI in Security Operations
AI agents that analyse event streams and run multi-step investigations are moving into production. They speed up everything from first triage to full investigation. Governance matters here. Teams should define which actions agents may take alone and which need approval.
Securing AI Workloads
AI tools and agents are new attack surfaces. They often hold privileged access and connect to sensitive data. They can be manipulated through prompt injection or poisoned data. The OWASP Top 10 for LLM Applications lists the main risks. AI endpoint security platforms are extending behavioural models to watch AI agent activity alongside human activity.
Calibrated Autonomy
AI works best under human governance. Mature programs let automation contain routine threats quickly. High-impact actions, such as isolating a critical production server, stay with a human. This balance is a design decision, not an afterthought.
How to Deploy AI Endpoint Security
A phased rollout reduces risk and builds trust. Our team usually recommends this sequence:
- Inventory endpoints. Include servers, cloud workloads, mobile devices and OT or IoT assets.
- Pilot in detect-only mode. Tune policies and exclusions before enabling automatic blocking.
- Enable autonomous response gradually. Start with low-risk actions such as killing known-bad processes.
- Integrate with SIEM, SOAR and identity tools. Make alerts flow into existing workflows.
- Review and tune regularly. Track detection quality, false positives and response times.
Align the program with a recognised framework such as the NIST Cybersecurity Framework. It gives a common language for governance, protection, detection, response and recovery. Our guide to cloud security integration shows how endpoint platforms fit into a wider cloud security architecture.
AI Endpoint Security Mistakes to Avoid
Even strong platforms underperform when the rollout is rushed. These are the AI endpoint security mistakes our team sees most often in evaluations and reviews:
- Leaving coverage gaps. Servers, cloud workloads and contractor devices are often missing from the agent rollout. Attackers look for exactly those gaps.
- Skipping tuning. Default policies can create noise. Untuned AI endpoint security quickly trains analysts to ignore alerts.
- Turning on full autonomy on day one. Aggressive automatic isolation can take down critical systems. Expand autonomy step by step.
- Ignoring identity. Many attacks use valid credentials. Endpoint data without identity context misses them.
- Treating it as a one-off project. AI endpoint security needs regular review as the estate, the threats and the business change.
Avoiding these mistakes is usually cheaper than switching vendors. Good AI endpoint security depends as much on process and integration as on the detection engine itself.
Where ICANIO Fits in AI Endpoint Security
ICANIO's DevOps and cloud engineering services help enterprises evaluate, integrate and operate AI endpoint security platforms alongside their existing cloud infrastructure. Typical work includes platform evaluation, endpoint detection and response integration with SIEM and SOAR, extended detection and response design for multi-cloud estates, and ongoing support for production deployments.
We are vendor-neutral on AI endpoint security. The right platform depends on your estate, your connectivity, your team's skills and your compliance obligations.
Conclusion
Signature antivirus was built for a slower threat landscape. AI endpoint security replaces file matching with behavioural detection and automated response. It combines four layers: next generation antivirus, endpoint detection and response, extended detection and response, and AI-assisted operations.
Deploy it in phases, keep humans in charge of high-impact actions, and integrate it with identity and zero trust controls. If you are reviewing your endpoint strategy, contact ICANIO to talk with our security and cloud engineering team.
References
- MITRE ATT&CK knowledge base
- NIST Cybersecurity Framework
- NIST SP 800-207: Zero Trust Architecture
- CISA: StopRansomware
- OWASP Top 10 for LLM Applications
- Wikipedia: Endpoint detection and response
Frequently asked questions
How does AI endpoint security differ from traditional antivirus?
Traditional antivirus matches files against a database of known malicious signatures, so it only catches threats it has seen before. AI endpoint security analyses behaviour instead. It learns what normal activity looks like for each device and user, then flags deviations in real time. That lets it detect zero-day exploits, fileless attacks and new malware that signature tools miss.
Can AI endpoint security replace human security analysts?
No. These platforms handle volume and speed: triaging large numbers of alerts, correlating attack chains and containing threats in seconds. Human analysts remain essential for judgement, threat hunting, governance and complex incidents. The best model in 2026 lets automation handle routine work while people supervise the system and make the high-impact decisions that need context.
What is ransomware rollback?
Ransomware rollback restores files that ransomware has encrypted to their pre-attack state, usually from protected local snapshots. Support differs between platforms: some offer it natively, others rely on integrations or separate backup tools. If ransomware recovery speed is a priority, test rollback during evaluation and keep independent, offline backups as well, since rollback is not a substitute for them.
How does AI endpoint security work when a device is offline?
It depends on the architecture. Platforms that run models on the device can keep detecting and responding without a connection. Platforms that rely more on cloud analysis may lose some detection depth until the device reconnects. For remote staff, branch offices or OT environments with poor connectivity, test offline behaviour before choosing a platform.
Is AI endpoint security suitable for small businesses?
Yes. Small businesses can benefit a lot from behavioral AI security and automated response, because they rarely have staff to watch alerts all day. Many vendors offer smaller tiers. Managed endpoint detection and response services also let small teams access enterprise-grade protection without building their own security operations centre from scratch.
What is the difference between EDR and XDR?
Endpoint detection and response focuses on endpoints, recording and investigating activity on laptops, servers and workloads. Extended detection and response adds telemetry from identity, email, network and cloud services, then correlates it in one platform. XDR helps detect attacks that move across several surfaces, which single-layer tools often see only in fragments.